


OUR Method
This is how we bring you into compliance.
80%
automated
Our platform automatically generates most of the documentation required by NIS 2: risk management, notification procedures, incident records.
5×
faster
Less waiting, less regulatory uncertainty: from the applicability assessment to the compliance plan, with the same rigor required by the NIS 2 Directive.
100%
success
We support you all the way to ACN registration: no missed deadlines, no missing documentation on 31 October 2026.
Network and Information Security Directive 2
Your company’s cybersecurity
is already in place. Make it NIS 2 compliant.

complete COMPLIANCE plan
We assess your specific case, then prepare the full plan up to the NIS 2 deadline.
We analyse your company’s sector, size and activities: whether NIS 2 applies to you or not, what you must do if it does, and by when. From there, we build the complete plan to be compliant by 31 October 2026.
WE START FROM WHAT YOU ALREADY HAVE
With ISO 27001 you are already well on your way. If you don’t have it, we build it for you.
Those who already have ISO 27001 start with an advantage: we check what is missing compared to the NIS 2 Directive and close the gaps together with your Lead Auditor. Those who don’t have it yet build it from here, with a single path that covers certification and regulatory compliance together.

COMPLIANCE that CONTINUES EVERY DAY
Keep your NIS 2 compliance, also after the 31 October 2026 deadline.
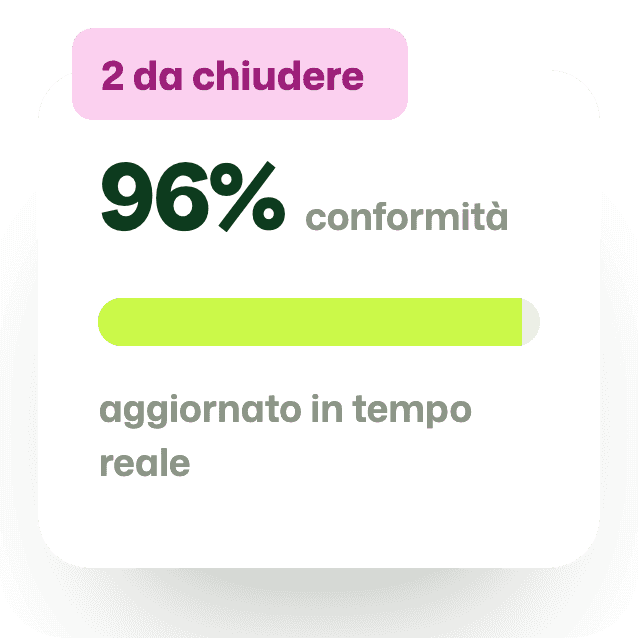
Registering with ACN is only the first step. NIS 2 requires you to keep risk management up to date and the incident notification procedure ready within 24 hours of the first alert. The platform monitors your compliance over time, your Lead Auditor steps in if anything drifts from the requirements.
CERTIFIED LEAD AUDITORS
We know NIS 2 deadline by deadline, obligation by obligation.
This is the team of certified Lead Auditors who will guide you through your NIS 2 compliance process.


complaion’s process
We’ll be with you up to the 31 October deadline. And beyond.
Documents
Documents
3 gaps
Upload documents
Let’s analyze what you already have, what’s missing and what you need to be ready.
Procedure n.123
3 ready
We write procedures
We build procedures, policies and records based on the way you actually work.
Compliant
Let’s do the Audit
We carry out the Internal Audit, produce the reports and check that everything is ready.

Ongoing compliance
Get the report
Complaion issues an official audit report as evidence in case of an ACN inspection.
Audit Report
NIS 2 Directive
COMPANY compliant with the nis 2 directive
Signed audit report, as proof of compliance.
Valid as evidence in case of an ACN inspection
Requested by clients and supply chain partners
Covers all technical requirements
Updated with every regulatory change
Client stories
Who has achieved NIS 2 compliance
with Complaion.


OFTEN COMBINED
Some ISO certifications make NIS 2 compliance easier.
Companies that must comply with the NIS 2 Directive often have other needs too: quality, safety, supply chain. Some ISO certifications answer more than one requirement at once.


FREQUENTLY ASKED QUESTIONS
Do you have any questions about NIS 2
or how Complaion can help you?
What is NIS 2 and why does it matter for my company?
NIS 2 is a European directive setting requirements for the security of network and information systems across the EU. It ensures that essential and important entities, particularly in critical sectors such as energy, transport and healthcare, take a robust and systematic approach to managing cybersecurity risk. It is key to demonstrating your commitment to protecting critical infrastructure, improving resilience against cyber threats and complying with EU network and information security rules.
How can you help my company achieve NIS 2 compliance?
Complaion automates up to 80% of the compliance process, significantly reducing the time and effort required. Our platform tracks progress and provides customizable templates to streamline the rollout of your compliance system.
How long does it usually take to achieve NIS 2 compliance with Complaion?
The time to reach NIS 2 compliance depends on the size, complexity and readiness of your organization. However, Complaion’s automation and streamlined processes can help you get there in a third of the usual time, with some companies becoming compliant in just a few weeks.
What support does Complaion offer during the NIS 2 compliance process?
Complaion provides dedicated support at every stage of the compliance process. This includes guidance from a Customer Success Manager and access to in-house NIS 2 experts who help you navigate the process, making sure you have the knowledge and resources for a successful compliance journey.
How do I start the NIS 2 compliance process with Complaion?
To start your NIS 2 compliance journey with Complaion, request a demo from our website. You will get an overview of our platform, its features and how we can tailor our services to your specific needs.
Do you support standards other than NIS 2?
Yes. Complaion supports a wide range of certifications, including ISO 9001, ISO 27001, ISO 27017, ISO 27018 and more. Our platform is designed to simplify certification across multiple standards, with integrations and features that streamline the process for different regulatory requirements.


